WAF OWASP CRS
Coraza powered by OWASP Core Rule Set v4: SQL injection, XSS, RCE, path traversal and anomaly scoring. Detection or blocking mode for each domain.
Web Application Firewall · Security Monitoring
Sentinel watches over your websites: it inspects every request, stops attacks before they touch the server and shows you everything in real time. WAF OWASP CRS engine, agent fleet, geo-blocking, instant alerts. Self-hosted, made in Italy.
Updating live data…
Sentinel in action
A real operating flow of our Sentinel infrastructure. The published data is aggregated and anonymised: no IP address, domain or customer is exposed.
Real fleet data
The WAF and agent recognise the abnormal request, the SSH attempt or threshold breach.
The protection applies the policy on the affected server, stopping the hostile origin before it continues.
The event reaches the central console with the server, rule and reason; the alerts notify the team.
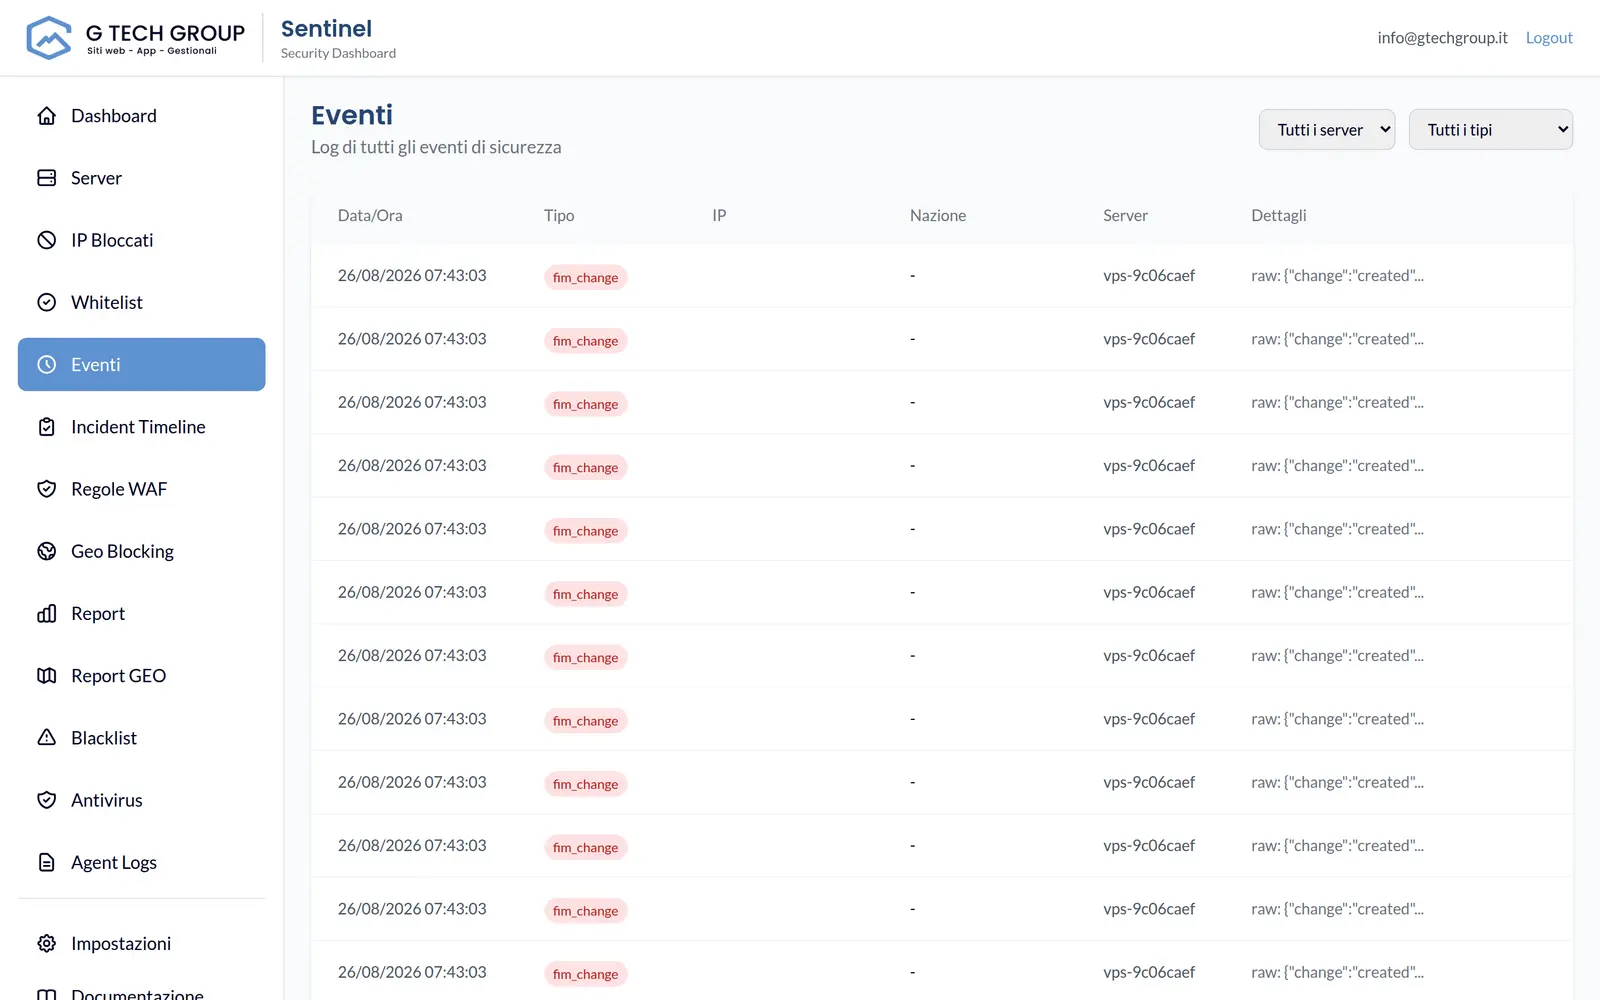
Interactive tour
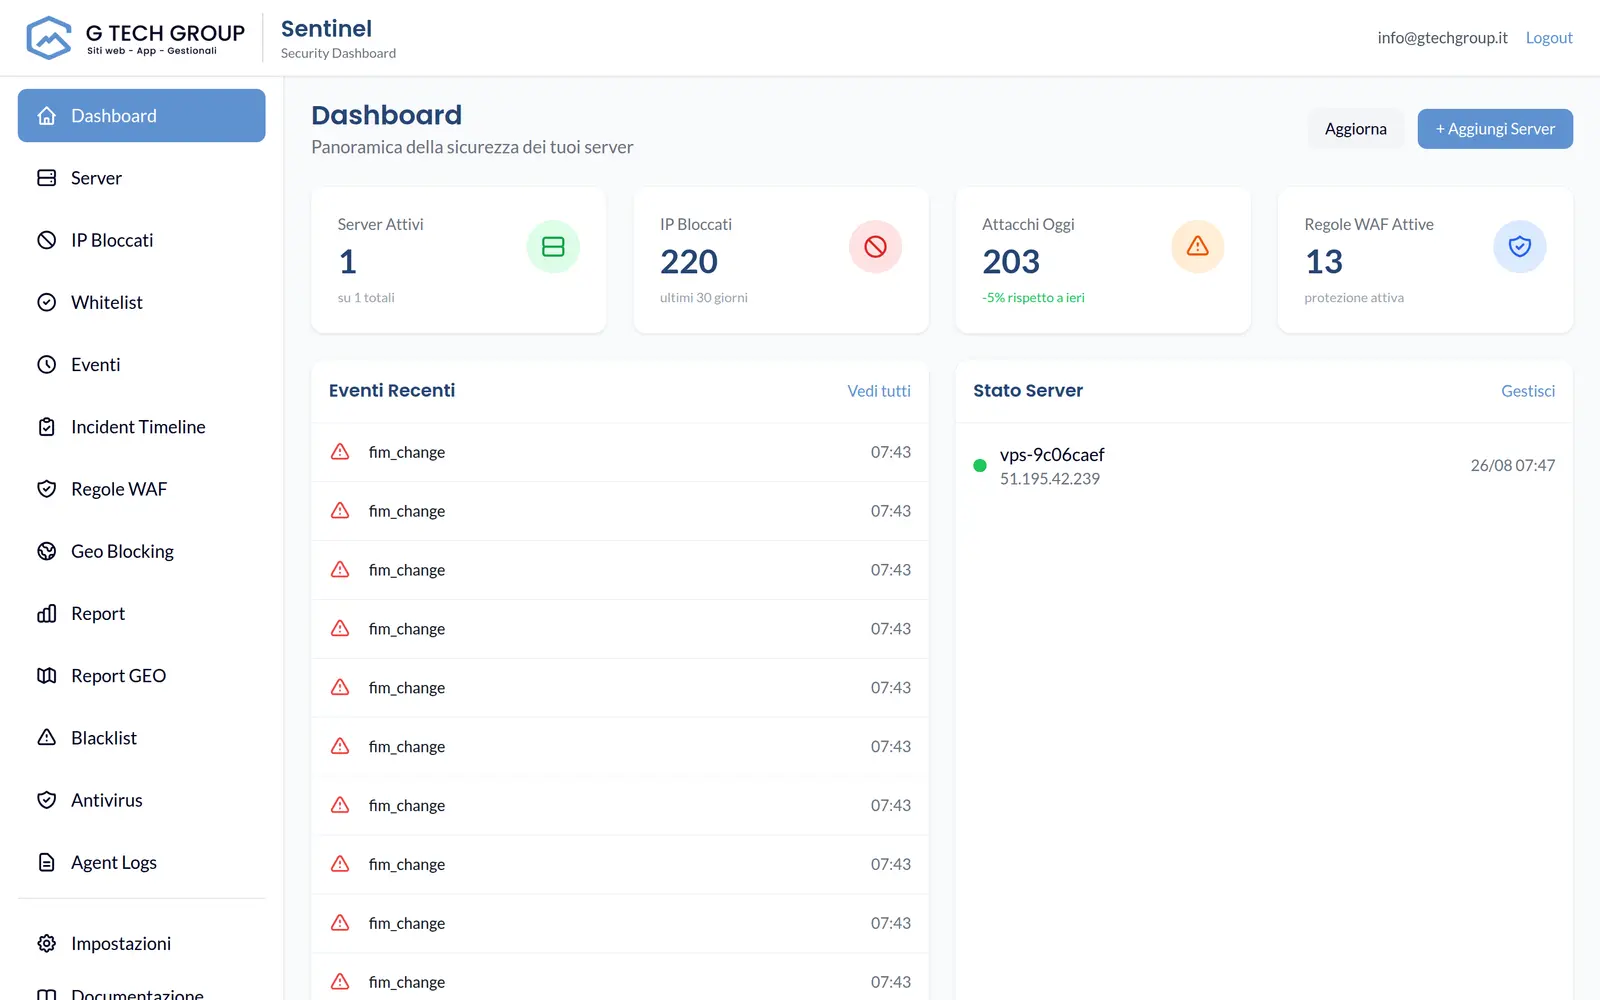
Explore real screenshots of the console: from the initial event to the block management, to the overall fleet view.
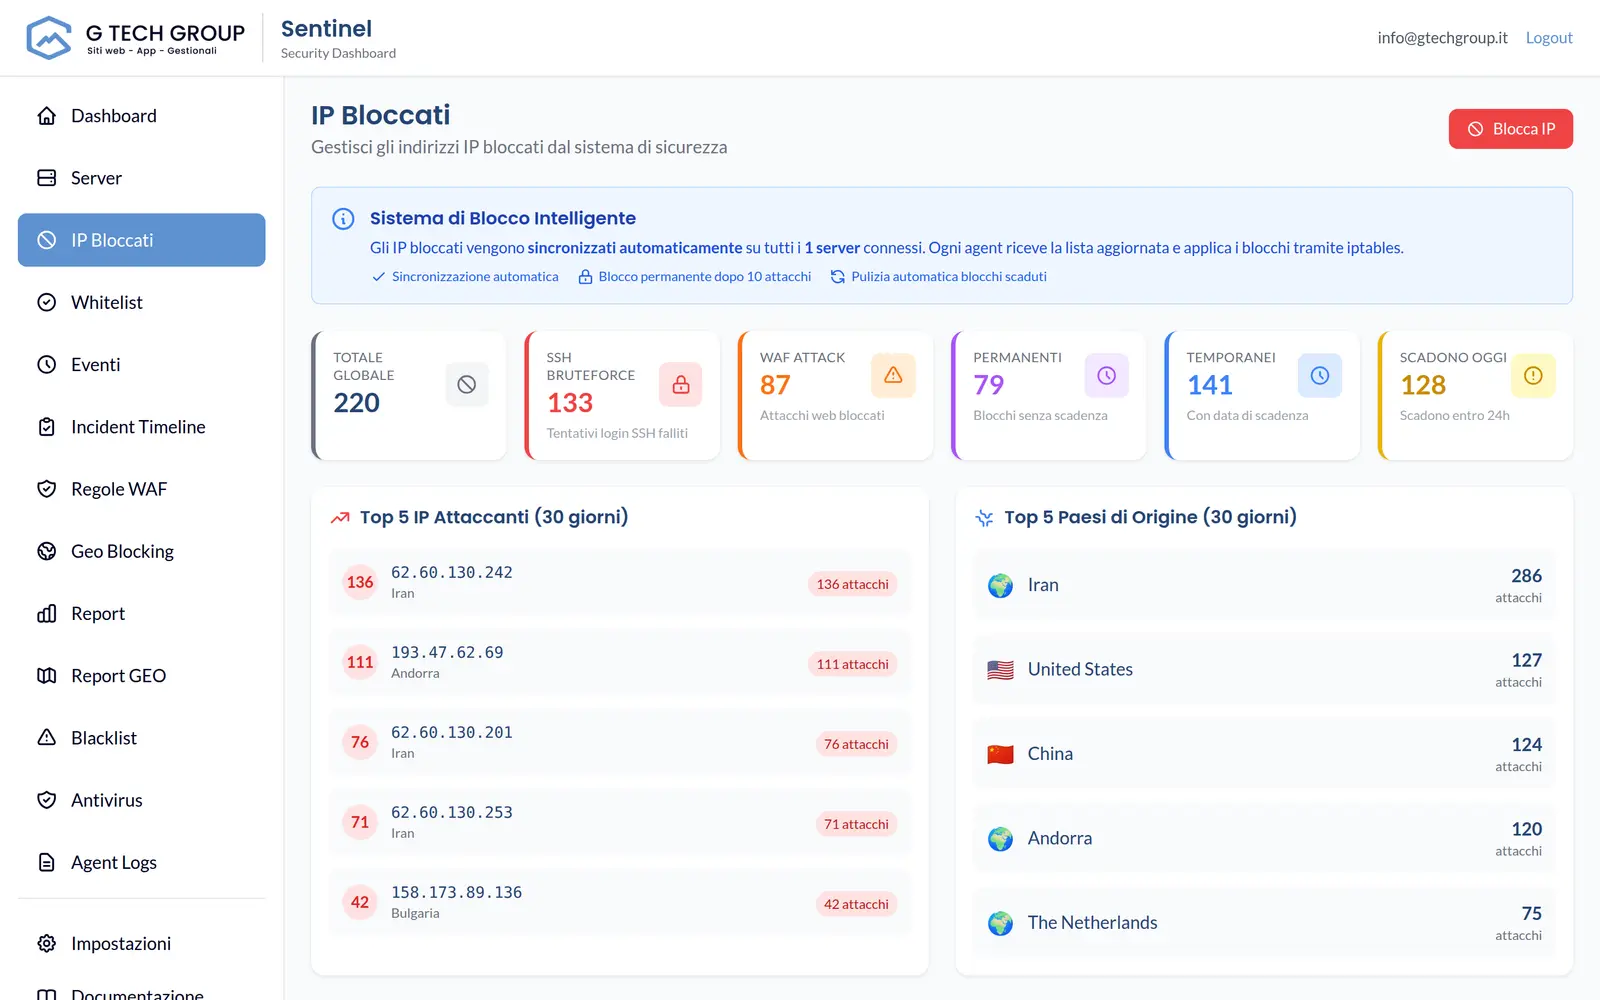
Protection
From L7 filtering to the local firewall, and from antivirus scanning to alerts on your phone.
Coraza powered by OWASP Core Rule Set v4: SQL injection, XSS, RCE, path traversal and anomaly scoring. Detection or blocking mode for each domain.
Each event, block and anomaly in live dashboard. Fleet logs are aggregated centrally.
Manage dozens of servers from one panel. Updates canary Gradual and anti-brick.
Block entire countries and malicious TLS fingerprints. Verified bots such as Google and Bing are recognised and allowed through.
Self-hosted push notifications (ntfy) and dedicated Android apps. You know right away when something is wrong.
ClamAV scanning and File Integrity Monitoring: detects malware and suspicious file changes.
Per-IP and global rate limiting with a JavaScript challenge: legitimate browsers pass while automated floods are stopped.
Monitor access attempts and Nginx, Apache or custom logs; block hostile IPs directly on the local firewall.
Learn more →Evaluate incoming IPs and check if your servers' public addresses are blacklisted.
Learn more →Separate viewer, operator and admin, secure access with TOTP and record sensitive operations.
Learn more →The core is self-hosted, with mTLS between agent and server and at-rest encrypted secrets. External integrations are optional and declared.
How it works
A lightweight reverse proxy puts the WAF in front of your sites. It inspects every request and blocks attacks locally, in milliseconds.
It collects events, synchronises rules and blocks over mTLS-protected gRPC, coordinates the fleet and retains the event history.
See everything in real time, create rules, manage updates and receive alerts from any device.
Why Sentinel
Developed by G Tech Group. Support in Italian, no black box.
The core runs on your servers without lock-ins. Only external integrations are optional and configurable.
Built with Go and Coraza without CGO: sub-millisecond latency and a minimal resource footprint.
Server-synchronised rules and safe canary updates across the entire fleet.
Tell us about your infrastructure: we verify compatibility and identify the most suitable annual plan.