One platform, every layer of defence.

From L7 application filtering and the local firewall to antivirus and mobile alerts: everything Sentinel does to protect your sites is explained in detail.

Protects

Stop hostile traffic before it reaches applications.

WAF, volume control, reputation and geographic rules work on the server that hosts the site.

Detect

Show attacks and changes that require attention.

Events, logs, malware scans and file integrity converge into a centralised view.

Coordinate

Manage multiple servers consistently.

Policies, agent status and gradual updates are managed from one console.

Web Application Firewall

Stop attacks before they reach your application.

The Coraza engine with OWASP Core Rule Set v4: inspect every HTTP request and stop SQL injection, XSS, RCE, path traversal and more, with anomaly scoring.
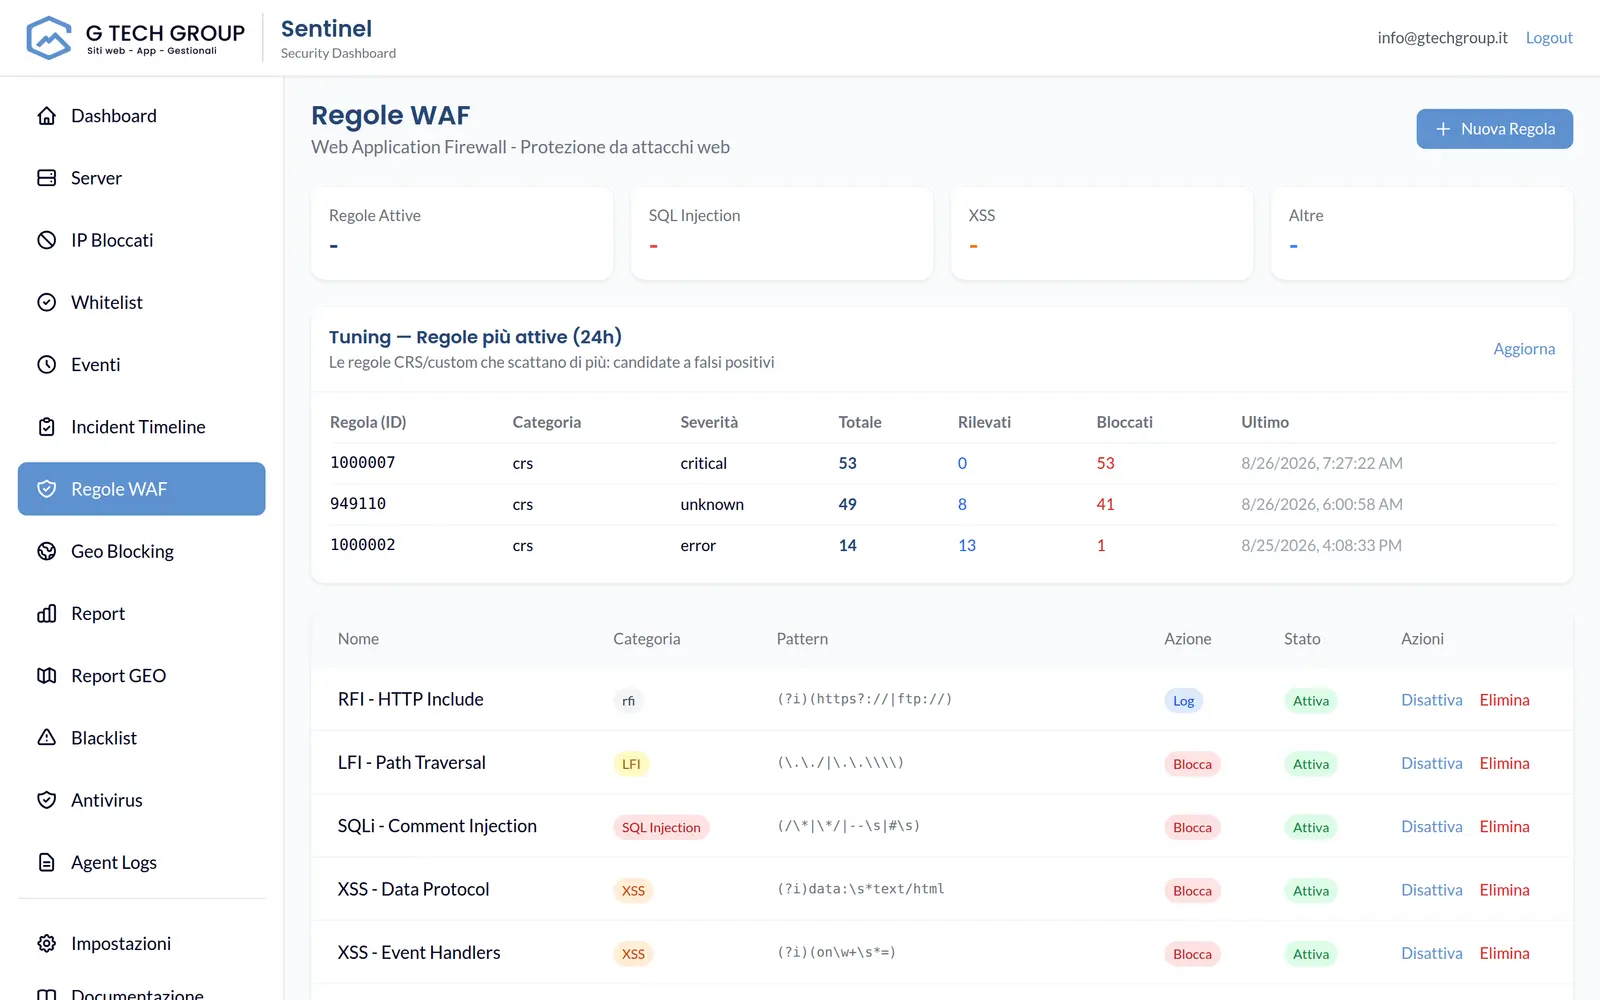
  • Detection or blocking, configurable by domain: first look, then block.
  • Custom rules in addition to CRS, synchronised by the server in real time.
  • False positives under control with tuning of the most active rules.
Learn more →
Sentinel dashboard real screen

DDoS L7 & Bot protection

Absorb application floods and expose disguised bots.

Per-IP and global rate limiting with token bucket, and a JavaScript challenge that separates real browsers from the bots: under attack, the real users pass while the flood is stopped.
  • JA4 TLS fingerprints with blocklist/allowlist of malicious clients.
  • Verified bots (Googlebot, Bingbot...) via reverse-DNS + forward-confirm.
  • "Under attack mode" implicit: activated only when needed.
Learn more →
Sentinel dashboard real screen

Geo-blocking & Reputation

Reduce the surface of the attack.

Block whole countries with local GeoIP database, manage blacklist/allowlisted IP addresses and evaluate the reputation IP source is all synchronized on the fleet.
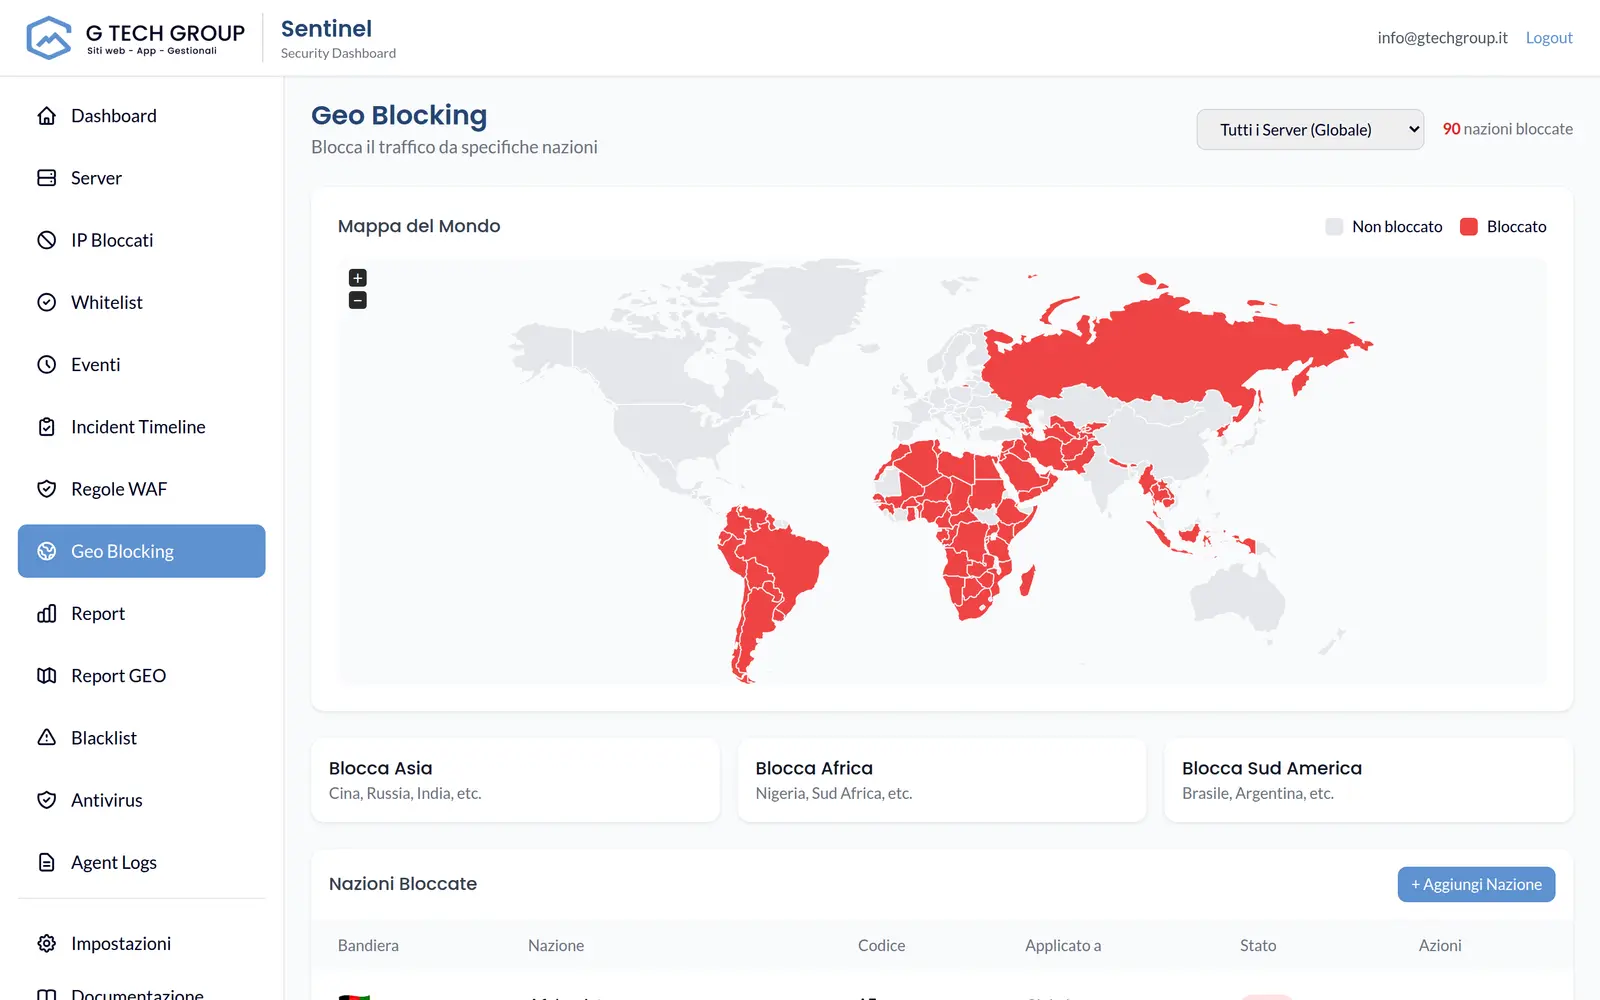
  • Policy per-domain: different countries for different sites.
  • Mode block or log to introduce the rules in safety.
  • Fail-open: If the GeoIP database is unavailable, traffic is not blocked by mistake.
Learn more →
Sentinel dashboard real screen

Antivirus & File Integrity

Malware and suspicious changes, spotted immediately.

Quick, full or custom scans with ClamAV optional hash lookup, plus File Integrity Monitoring on critical paths.
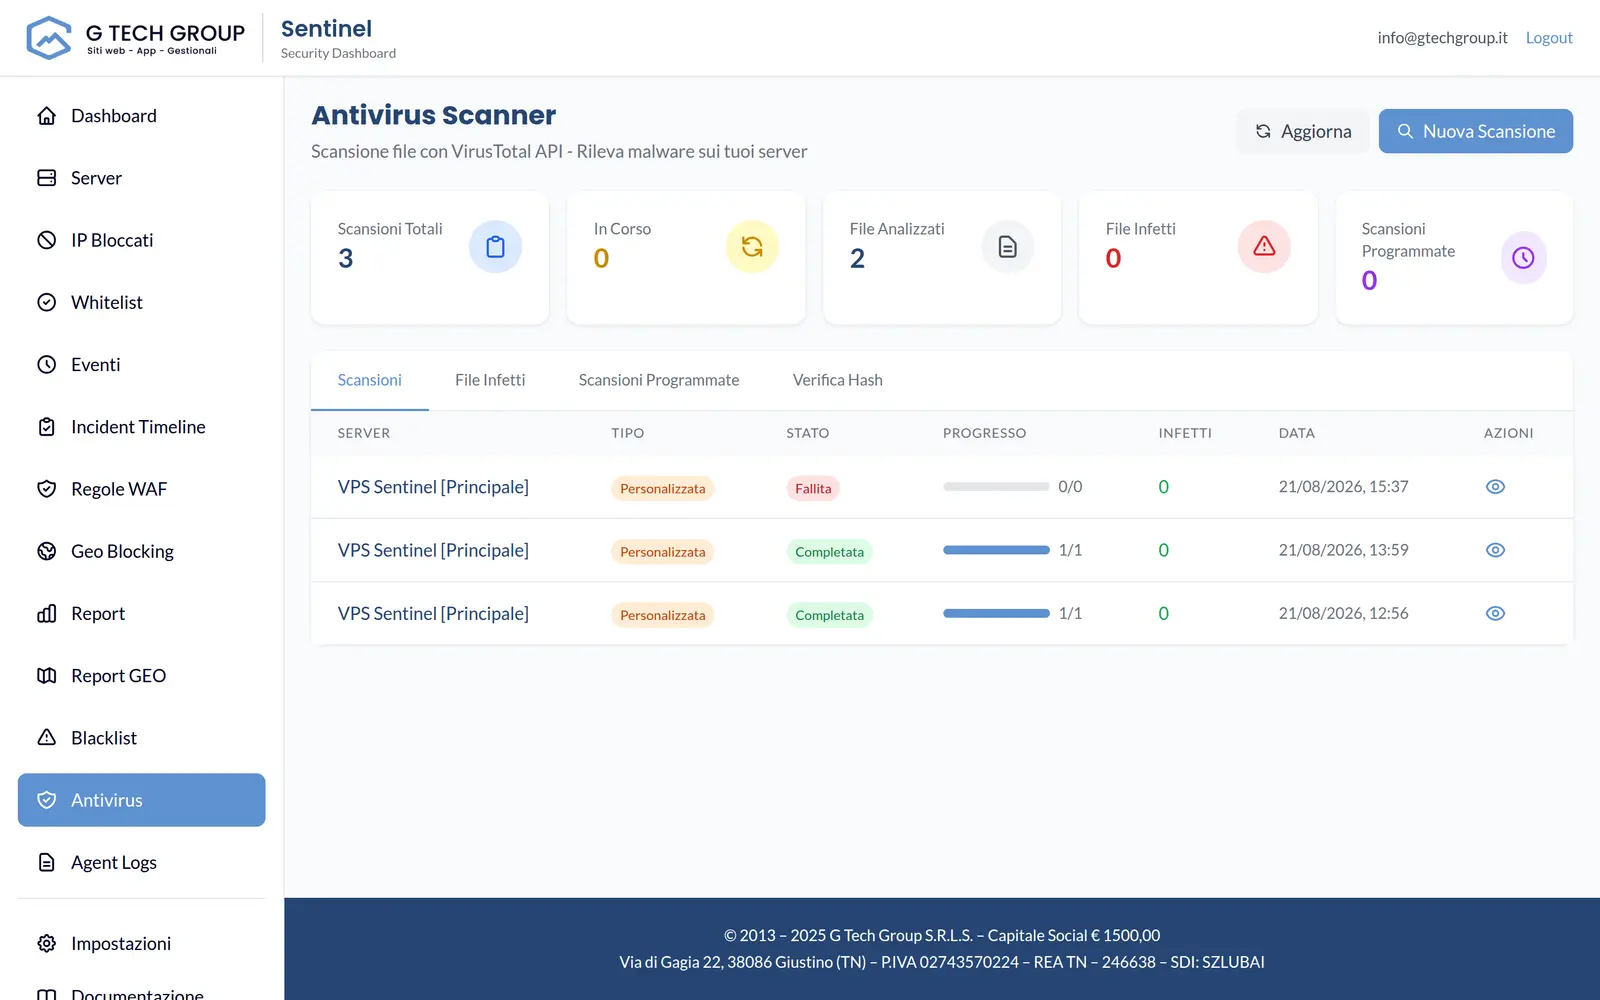
  • Integrated scanner using clamd (streaming scans).
  • FIM: hashes and permissions are monitored, with alerts for every relevant change.
  • Scheduled scans, progress, results and false positives in the panel.
Learn more →
Sentinel dashboard real screen

Real-time monitoring & alerts

See every event as it happens.

Event dashboard, aggregated logs, incident timeline, geographical report and CSV export, with self-hosted push alerts via ntfy and optional email summaries.
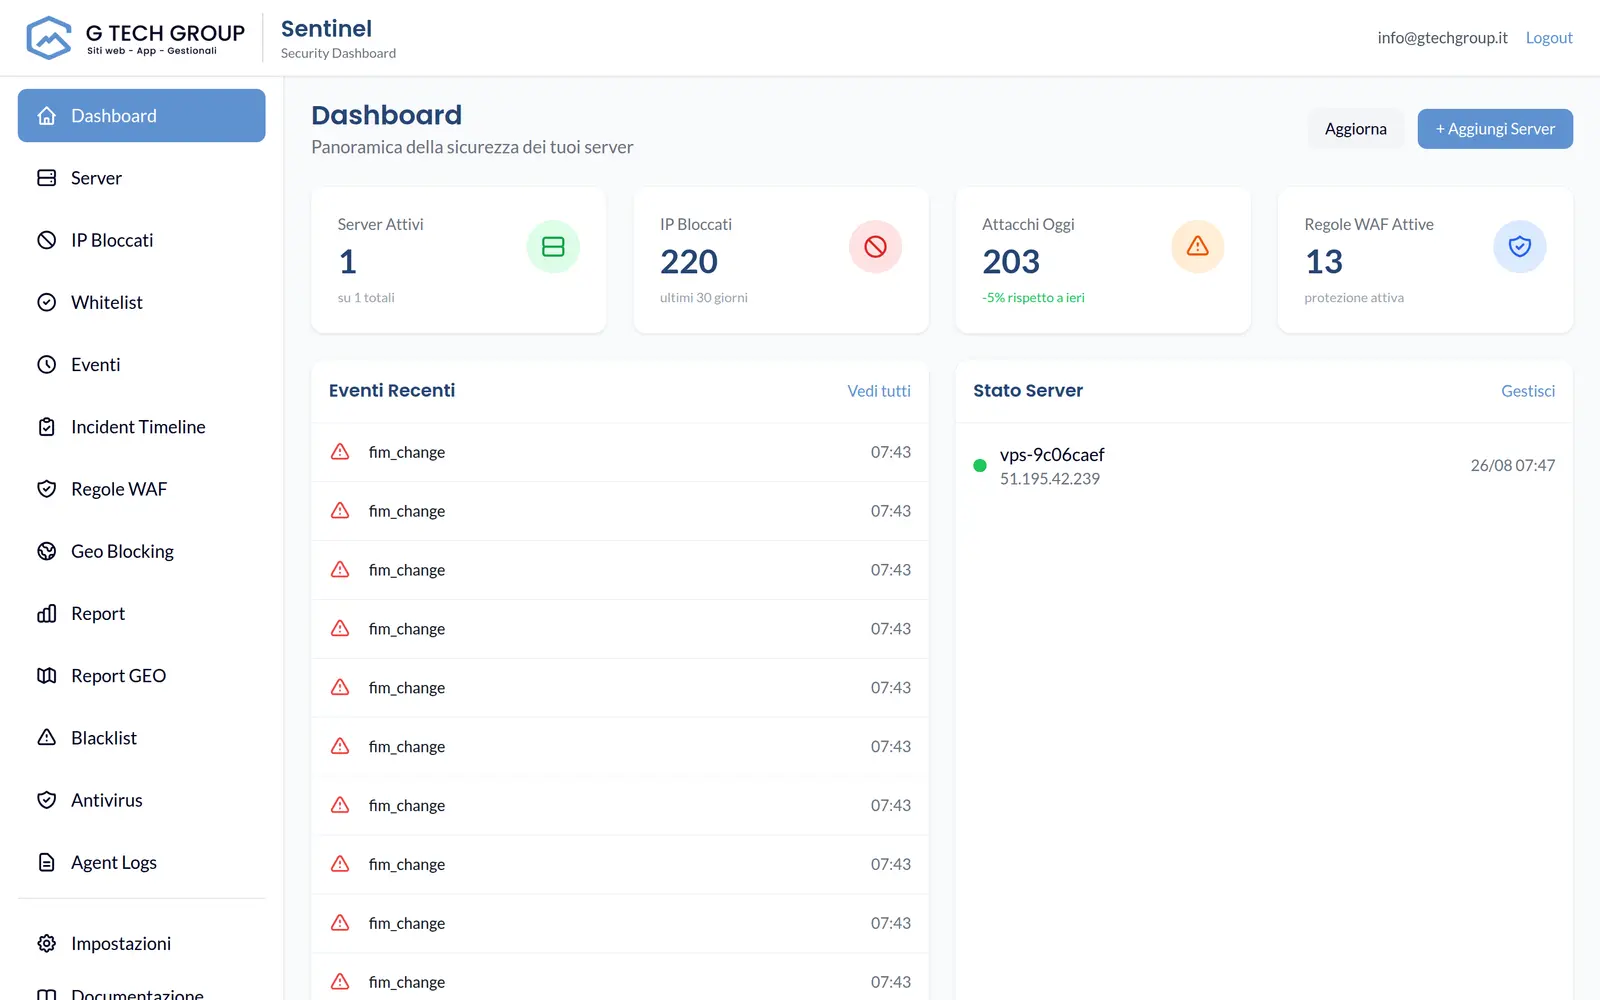
  • WAF events, blocks, anomalies and incidents in real time.
  • Aggregated logs of all agents, in one place.
  • Notifications on ntfy, Android apps and SMTP reports when configured.
Learn more →
Sentinel dashboard real screen

Fleet Management & Updates

Manage dozens of agents without "bricking" servers.

Manage the entire fleet from a single console, with anti-brick canary updates: the update starts on a subset and continues on the rest only if the canary remains healthy.
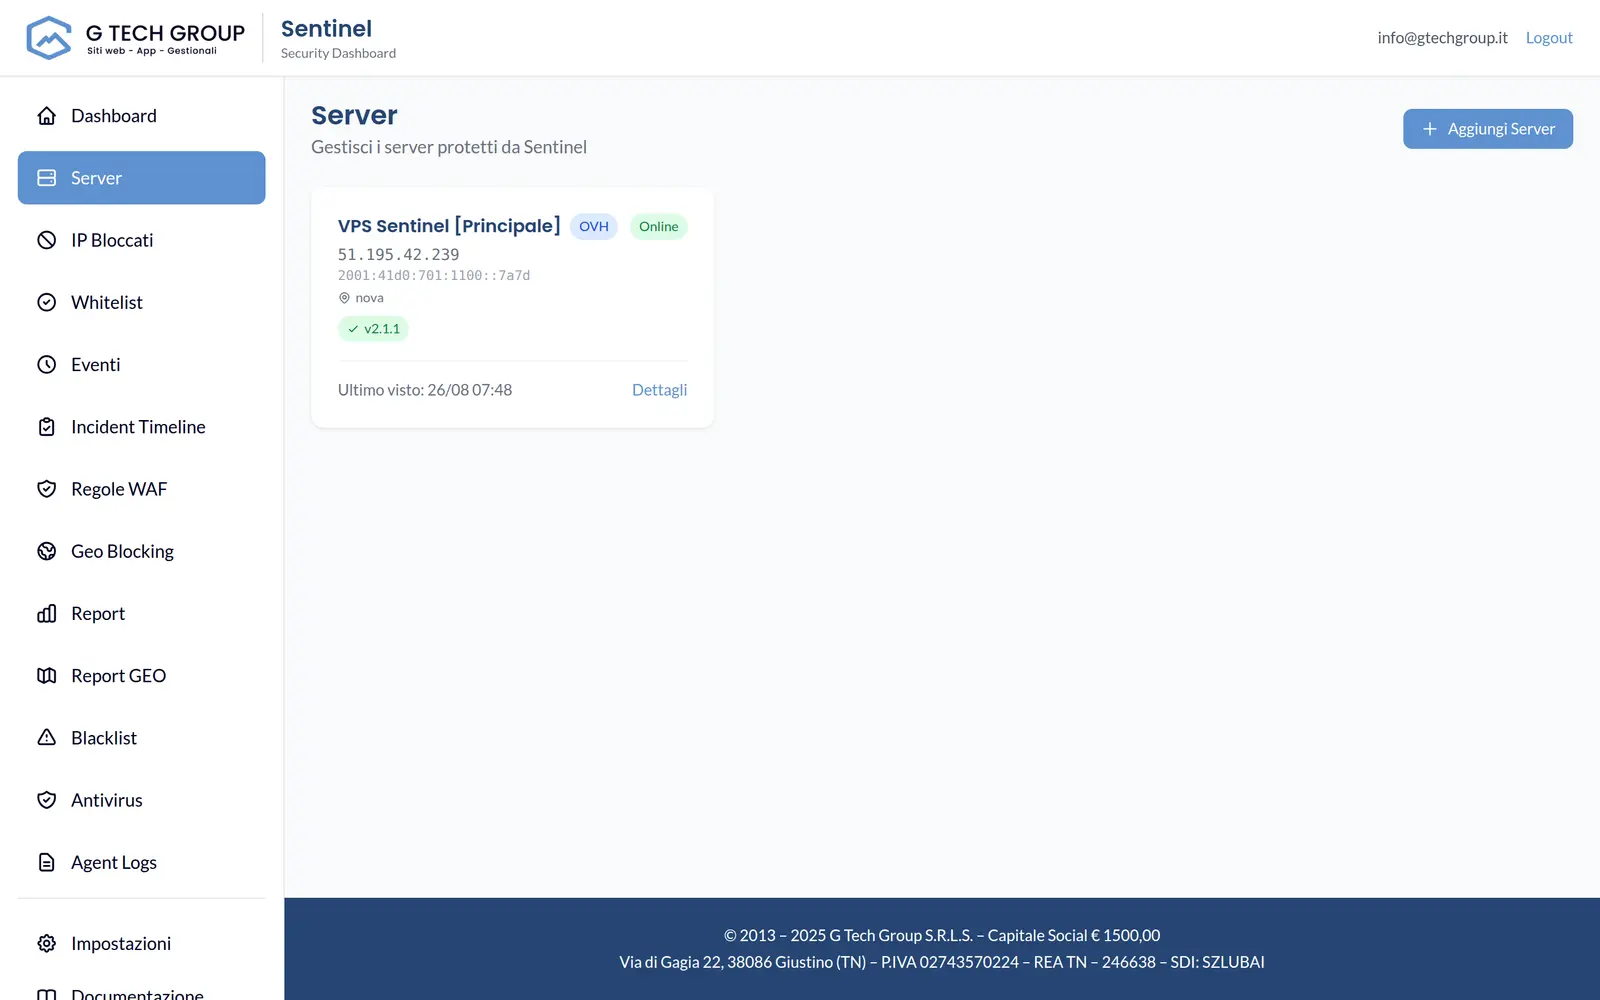
  • Onboarding, system metrics and one console for all servers protected.
  • Rollout canary waves with health check.
  • Watchdog and self-recovery of the agent: protection remains available.
Learn more →
Sentinel dashboard real screen

Host & Access Protection

SSH and application logs become an active defence.

The agent monitors authentication attempts and Nginx, Apache or custom application logs. At the configured threshold, it applies the block on the local firewall and records the event on the dashboard.
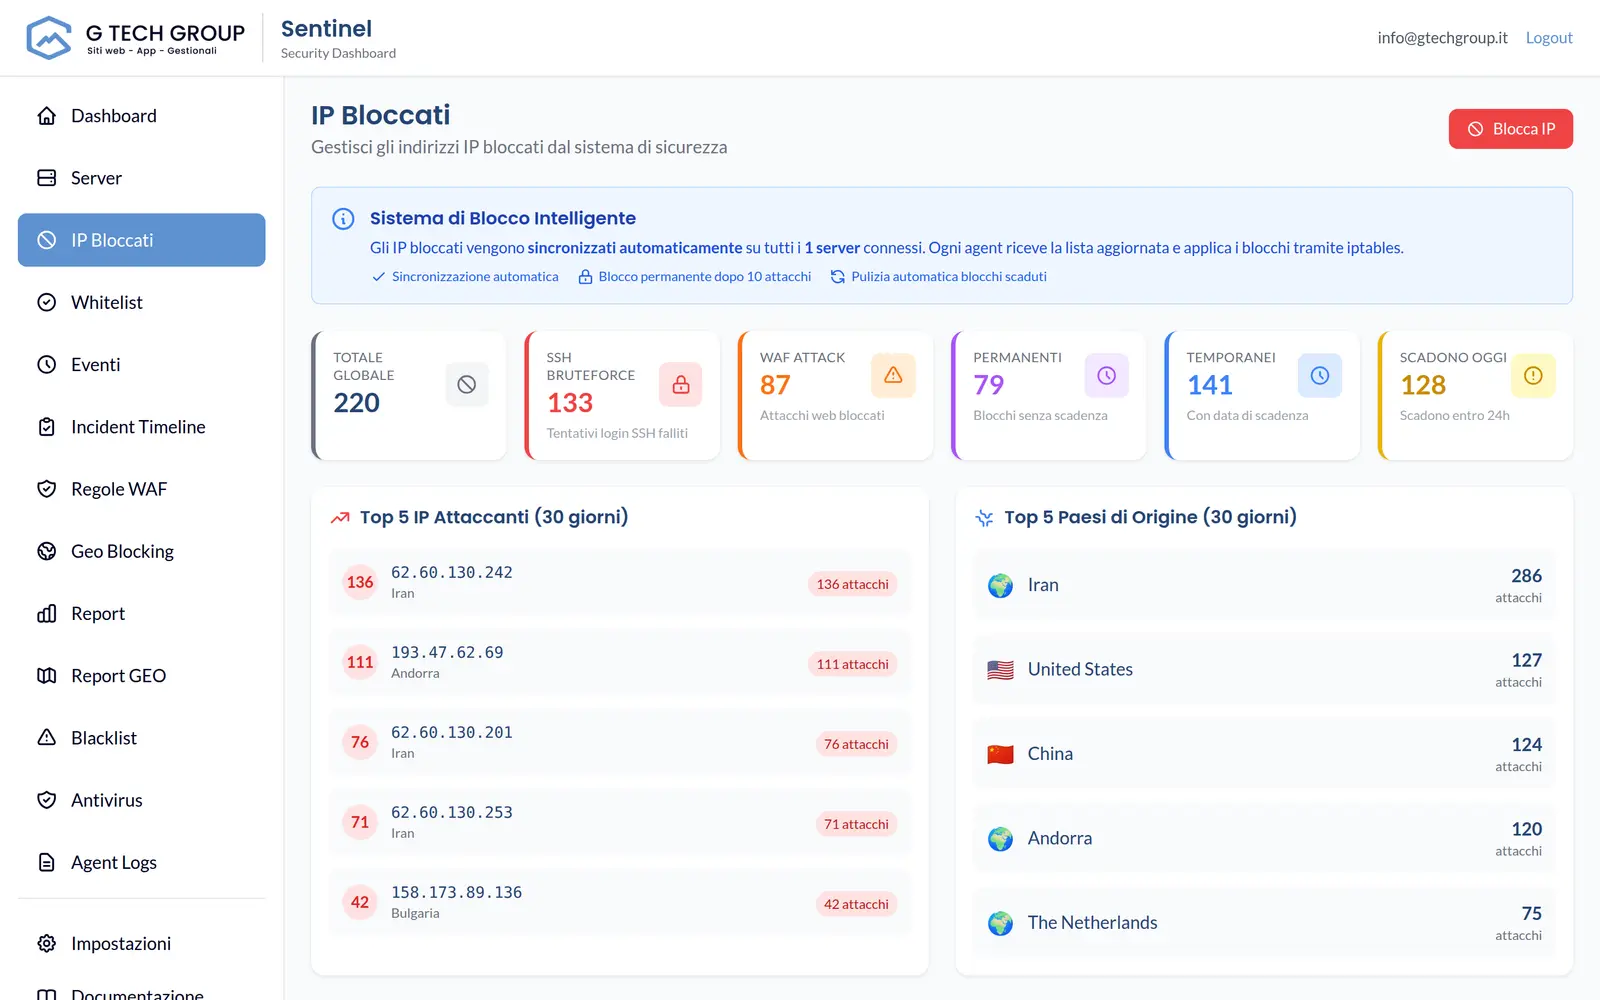
  • Brute-force SSH and Windows authentication.
  • Watcher Nginx, Apache and custom patterns.
  • Temporary or permanent blocks, with allowlist prioritys.
Learn more →
Blocked IP addresses and server protection in the Sentinel dashboard

Threat intelligence & DNSBL

Assess incoming sources and monitor the host's reputation.

Feed, DNSBL and local history contribute to the source IP score. A separate check periodically checks whether your servers' public IPs are reported in DNS blacklists.

  • Reputation score from 0 to 100 and shadow mode.
  • HTTPS feeds with blocking or monitoring actions.
  • Fleet-wide DNSBL checks and delisting guidance.
Learn more →
Threat intelligence and IP reputation in Sentinel

Panel Governance

Separate access, add a second factor and retain a trace of every operation.

Viewer, operator and admin also have separate permissions at API level. The login supports TOTP and anti-abuse protections; mutations are recorded in the audit log.

  • Server-side roles and privileges.
  • 2FA TOTP and personal password change.
  • Login audits, successful operations, denied or in error.
Learn more →
Sentinel Control Panel

How it works

Three pieces, all inside your infrastructure.

User traffic is processed locally. Hash lookups, DNSBL, feed and SMTP are optional integrations and are only used when configured.

01

The agent on your server

A lightweight reverse proxy in Go applies WAF, rate-limit, JA4, antivirus and FIM. It inspects and blocks locally, in milliseconds.

02

The central server

It collects events and logs, synchronizes rules and blocks via gRPC mTLS, orchestrates the fleet and retains the event history.

03

Your dashboard

Monitor everything in real time, create rules, manage updates, and receive alerts from any device.

mTLS end-to-endEncrypted secrets at-restAnti-brick Rollout Canary

Do you want to see them in action?

We show you Sentinel live on your infrastructure and tailor it.